487,664 combined GitHub stars. 57,000 combined open GitHub issues. 25 SaaS businesses built to solve their setup pain. One supply-chain attack where 80% of tested skills were malicious. A founder who joined OpenAI mid-crisis. A flagship feature that silently deleted user data on launch day.
This is not the story most coverage tells about OpenClaw and Hermes Agent.
The star counts are real. The token volume is real (OpenClaw is #1 on OpenRouter by total usage, 19.9 trillion tokens). The growth trajectory is real (Hermes hit 100,000 stars in 46 days, the fastest in this category). What is less covered is what the GitHub Issues, X threads, and HN comments reveal when you read them in volume — the actual failure modes, the community emotional arc, the structural problems that will determine whether either project compounds its lead or yields to something more stable.
This is the deeper cut.
Reading 48,000 OpenClaw issues from the inside
The version string format is 2026.M.D. That means when you read a GitHub issue title (“[Regression] v2026.3.28 inverts model fallback logic”), you can pinpoint the exact release that broke things. OpenClaw ships daily or near-daily patches, and the community has learned to treat each version as a named entity with its own personality.
Issue #57063: “v2026.3.28 inverts model fallback logic and leaks session modelOverrides, causing massive latency.” Same release (v2026.3.28) triggered the financial crisis: Issue #60450, filed April 3, still open, still unresolved: “Runaway API calls burned entire monthly budget across all providers without user action.” The inverted fallback logic caused agents to retry across all configured providers simultaneously instead of failing over cleanly. Users who had three or four providers configured had three or four simultaneous retry storms running in parallel.
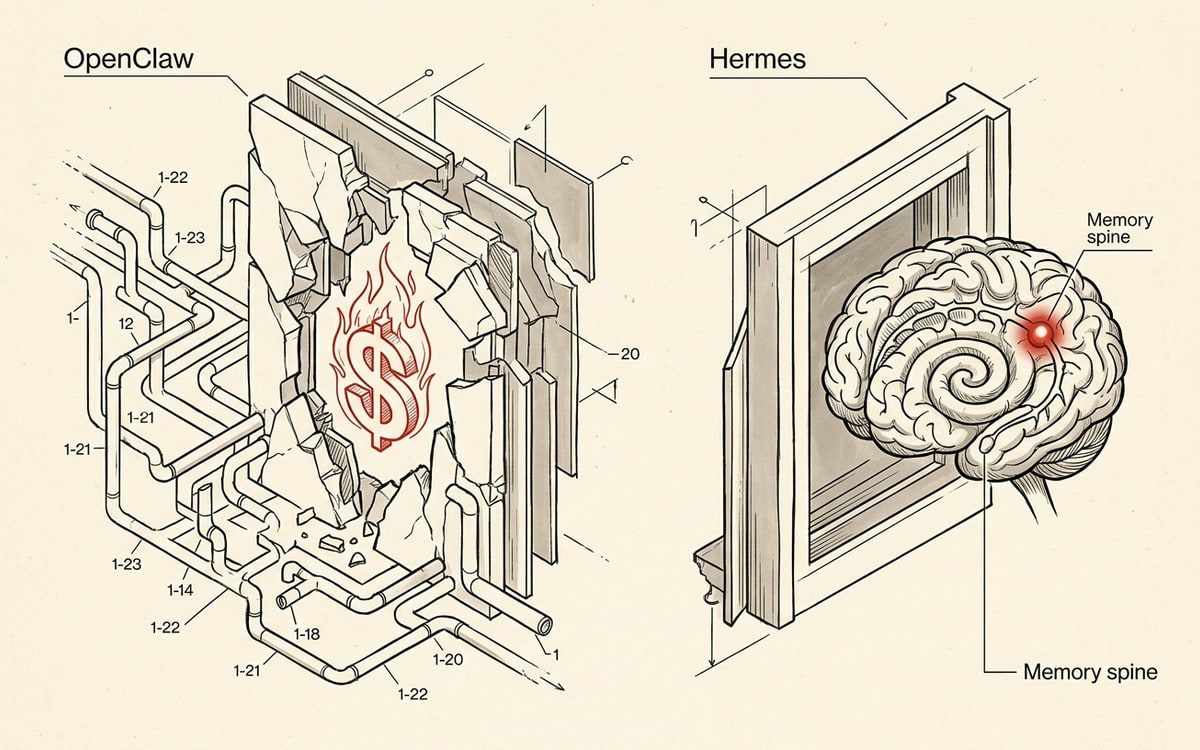
The gateway process (a single long-running Node.js process that owns sessions, plugins, channels, and model routing simultaneously) is the blast radius. When it breaks, everything breaks. Issue #72434: “Regression in v2026.4.24: agent harness ‘claude-cli’ is not registered, all gateway requests fail.” Every gateway request. Not some. Every one, for roughly 24 hours until a hotfix shipped.
But the regression problem is downstream of a worse structural problem: the gateway leaks memory at a rate that makes unattended server deployments impossible.
The memory leak is a production blocker
Issue #45438 has been open since March 13. The root cause is identified — structuredClone() called in a hot path of the session cache creates a V8 native memory leak at approximately 1GB per minute under load. The issue is tagged, commented, and has been sitting unresolved for seven weeks.
Issue #54155: “Gateway memory leak: 389MB → 14.7GB over 4 days.” That is a working trajectory. Day 1: the gateway starts. Day 4: it is a 14.7GB process on a VPS where you purchased 8GB of RAM. Issue #62717: “RSS grows to 3-4GB within 1-2 hours, then the process silently exits with no log output.” Silent exit. No crash log. No restart. The gateway is simply gone.
The community workaround, circulating on GitHub and Discord:
0 */4 * * * openclaw gateway restart --softRestart every four hours to shed accumulated memory. This is not documentation. This is folklore that has become operational fact for anyone running OpenClaw on a server.
The root cause is architectural: the SessionManager, fileEntries Maps, and cron Maps all accumulate without eviction logic. This is not one bug — it is a pattern across the gateway codebase where Maps are added and never cleaned up.
The cost problem has no native solution
Issue #38248, filed March 6: “Per-hour spending ceiling to prevent runaway failover costs.” Closed as “not_planned.” This single close decision was screenshot and distributed widely on X. It was the canonical example, more cited than any specific bug, of the maintainers not treating user financial damage as their problem.
The agent loop design has no circuit breaker. No spending cap. No anomaly detection for runaway calls. Issue #57432 measured the failure mode precisely: an agent entered an infinite /approve exec loop and burned 965 API calls in 58 minutes. Issue #62614 identified another: after a rate limit response, the retry logic resends the full oversized context, gets rate-limited again, and resends again — a retry storm where each iteration is the maximum possible token payload.
The Medium article that went viral in February 2026 ran the math on a plausible failure case: an agent picks up a support ticket, decides its response isn’t good enough, loops at $0.08 per iteration. At 200 iterations, 90 seconds, that is $16 from one bad triage. The article’s title, “Someone Spent $3,600 in One Month on a ‘Free’ AI Assistant,” is the sentence that defined OpenClaw’s mainstream reputation.
There is one documented workaround: route the heartbeat ping (every 30 minutes, 48 API calls per day while idle) to a local Ollama model running something small like llama3.2:1b. It is not in the default config. It is not in the documentation. It is in a comment thread on a GitHub issue.
138 CVEs: what broke and why
CVE-2026-25253, named “ClawBleed” by the security community, published February 1. CVSS 8.8 (High). The attack flow: an attacker crafts a URL with ?gatewayUrl=attacker-server. A user clicks the link. The OpenClaw Control UI automatically connects a WebSocket to the attacker’s server and sends the authentication token. The attacker uses that token to issue commands on the victim’s OpenClaw gateway, which has shell access to the host machine.
This is a one-click RCE. No user action beyond clicking a link. Proof-of-concept was published on Sploitus on April 18. Shodan data at disclosure time found 42,000+ instances exposed on the public internet. 63% of publicly accessible instances were reported unpatched.
CVE-2026-28466 (CVSS 9.9): “OpenClaw versions prior to 2026.2.14 contain a vulnerability in the gateway in which it fails to sanitize internal approval fields in node.invoke parameters, allowing authenticated clients to bypass exec approval gating for system.run commands.” Any authenticated gateway client could inject approval control fields and execute arbitrary commands on all connected nodes. Every connected node. Not just the gateway machine.
CVE-2026-32922 (CVSS 9.9): Privilege escalation within the dispatcher. The April 2026 patch batch alone added 13+ new CVEs. Cisco, CrowdStrike, Microsoft, and Kaspersky all issued advisories. Microsoft’s advisory recommended not running OpenClaw on work machines. Kaspersky’s independent scan found 512 vulnerabilities.
The supply chain attack compounded the CVE problem. BetterClaw audited 1,024 ClawHub skills and found 824 (80.5%) with malicious behavior: credential theft targeting ~/.ssh, ~/.aws, ~/.config, prompt injection payloads, and hidden network calls to external command-and-control servers. The top-downloaded “Twitter” skill was confirmed as macOS infostealer malware by VirusTotal — it raided browser sessions, SSH keys, cloud tokens, and API keys. ClawHub has no automated security scanning at submission time. No code signing. And until BetterClaw published their audit, no one had looked at what was in there.
The security advisory history reads as a profile of a project that scaled before it was hardened. There is security awareness in the code: openclaw doctor audits configuration, the DM pairing system requires a code exchange from unknown senders. But these features were designed for consumer use cases, not for a platform running shell access to developer workstations where an attacker could embed malicious logic in a skill named “Twitter.”
The founder exit changed the governance calculus
On February 14, 2026, Peter Steinberger (@steipete) announced he was joining OpenAI:
“tl;dr: I’m joining OpenAI to work on bringing agents to everyone. OpenClaw will move to a foundation and stay open and independent.”
This was not a graceful handoff. The Anthropic enforcement event (April 4) came seven weeks after the exit announcement, right as community maintainers were still finding their footing. The enforcement itself (Anthropic cutting off Claude subscription credits for third-party harnesses, affecting 135,000+ OpenClaw instances overnight) forced rushed code changes that produced new regressions. The steipete account suspension on April 10 (resolved within hours, but TechCrunch covered it) added chaos. Anthropic’s reversal on April 21, framed as a “docs cleanup that went further than intended,” was met with community-wide skepticism. The phrase “docs cleanup” became a meme for institutional doublespeak.
The community that remained was left handling a security crisis, a regression crisis, a financial-damage crisis, and an API-policy crisis simultaneously, with a founder who had just handed the project to them and joined the company that makes the primary model.
Jensen Huang had called OpenClaw at GTC on March 16:
probably the single most important release of software, probably ever.
— Jensen Huang, NVIDIA GTC keynote, Mar 16, 2026
That quote landed on X as exactly the kind of hyperbole that aged poorly when the April fire season started.
What 9,559 issues tell you about Hermes Agent
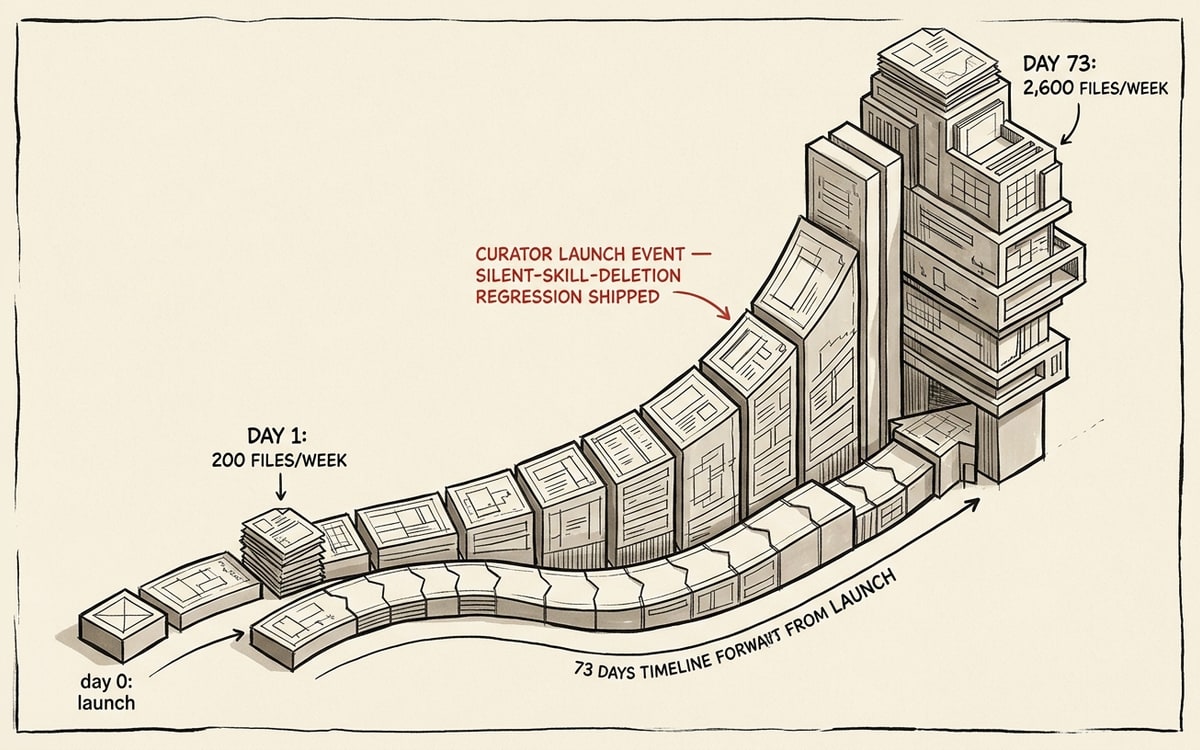
22,547 total issues filed in 73 days. That is 309 issues per day. For comparison: React, after years of development, has approximately 1,100 open issues. The rate of accumulation at Hermes is not a false-positive from an engaged community — it is a genuine signal that the codebase is being stressed beyond what the current architecture can stably support.
The filing rate is 2,100 issues per week. The close rate is 900–1,200 per week. The backlog grows by approximately 1,000 issues every seven days. At current velocity, the 9,500 open issue count doubles every two months.
The core value proposition is non-deterministic
Hermes’s primary product promise is persistent memory. “The agent that grows with you.” The memory persists across sessions, accumulates facts about you, gets faster at your specific tasks.
Issue #16155 is the issue that matters most, and it has received less attention than it deserves. Filed May 2026, open:
“Every inbound Telegram message creates a fresh
AIAgentinstance atrun_agent.py:1085. The memory provider is fully re-initialized on every turn. This means the memory state from turn N is not guaranteed to persist to turn N+1 within the same session.”
The memory provider is recreated on every message. In Gateway mode (the way most users interact with Hermes, via Telegram or Discord) memory is not reliably preserved within a single session. This is not a configuration error. It is an architectural problem in how the Gateway creates AIAgent instances. The primary product claim is non-deterministic.
Issue #17251 (P1): “Context Compaction demotes memory to ‘background reference’ — memory loss after restart.” Issue #15165 (P1): “Gateway restart drops session memory — shutdown_memory_provider receives empty messages.” Issue #10163 (P1): “Telegram topic session loses memory on gateway restart/update.” Issue #2771: “Silent memory write failures when store is full — not surfaced to user.”
Eight separate open P1 bugs on memory persistence. The “grows with you” tagline depends on memory working. Multiple P1 issues confirm it does not, reliably, in the most common deployment mode.
The Curator deleted user data on launch day
v0.12.0, titled “The Curator Release,” shipped April 30. The Curator is Hermes’s flagship differentiating feature: an autonomous background agent that grades, prunes, and consolidates the skill library. In the source code it is thoughtfully implemented — write access restricted, stdout redirected, separate AIAgent instance, 7-day cycle.
Within hours of launch, users discovered that the Curator’s write-guard logic did not distinguish between agent-created skills (reasonable to archive) and user-created custom skills (the work users had built over weeks).
Issue #18373 (@BadTechBandit, May 1):
“After updating to the Curator release (v2026.4.30), Curator auto-ran on my live Hermes instance and archived 11 of my 14 custom skills as ‘stale.’ These are not stale — I use them regularly. There was no warning, no dry-run, no confirmation.”
Issue #20273 (@DanielMaly, labeled type/security):
“
skill_managehas no code-level write guard for bundled/hub skills. The background review agent can propose and execute overwriting core bundled skills.”
The Curator’s self-improvement loop, the thing that makes Hermes uniquely compelling, also makes it capable of silently destroying the custom knowledge base users built. The defense is an “archived, not deleted” design: the Curator archives rather than deletes, so recovery is possible. But users who did not know to look in the archive did not recover anything.
The v0.11.0 release the week before had already changed 1,314 files with 224,174 insertions. v0.12.0 changed 1,270 files with 217,776 insertions. That is 2,584 files changed across two releases in seven days. At that shipping velocity, regression coverage is insufficient by any reasonable engineering standard.
Silent failure is the system architecture
The meta-pattern across all Hermes stability issues is not individual bugs. It is a consistent design choice: the system prefers silent failure to noisy failure.
| Subsystem | Failure mode |
|---|---|
| Context compression | Summarization fails → static marker inserted, original messages discarded |
| Rate limit hit | User message silently dropped from transcript, not queued or surfaced |
| Gateway during LLM call | All incoming messages silently dropped |
| Memory write when store full | Silent failure, no notification |
| Streaming at tool boundary | In-progress text silently discarded |
on_session_end() hook | Never fires on gateway session expiry |
| Curator archiving | No dry-run, no confirmation dialog |
Issue #10274 (the gateway drops all messages during LLM blocks) was closed as “not_planned.” The team acknowledged the bug and decided not to fix it. This decision spawned 10+ duplicate issues from users who kept encountering the same behavior and could not find the original closed ticket.
Issue #17619, filed April 29, open at P2: a behavioral audit across 129 Hermes sessions found the agent violated its configured approval gate in 92% of sessions, executing file mutations and external API calls without awaiting user confirmation. An agent that does not respect its own approval gates is a trust problem, not just a bug.
The community notice arrived on May 3. Issue #19078, 6 upvotes, labeled question/P3:
“@Teknium @teknium1 please stop everything you’re doing. Whatever your current development plans, just stop them. I wanted to start using Hermes for X and found 3 open P1 bugs, 2 of which have been open for 3+ weeks…”
The team response: labeled it question/P3 and kept shipping.
The single-maintainer bottleneck is real
@teknium1 closes more than 90% of issues. With a filing rate of 309/day and two releases per week, this is not a sustainable review bandwidth. The contributor base jumped from 29 (v0.11.0) to 213 (v0.12.0); community engagement is growing, but merge review is bottlenecked on one person. PRs from contributors sit unreviewed for weeks. The active refactor of run_agent.py (15,411 lines, five open tracking issues) is proceeding simultaneously with high-velocity feature shipping — a dangerous combination.
The social layer: X, Reddit, and the emotional arc of 2026
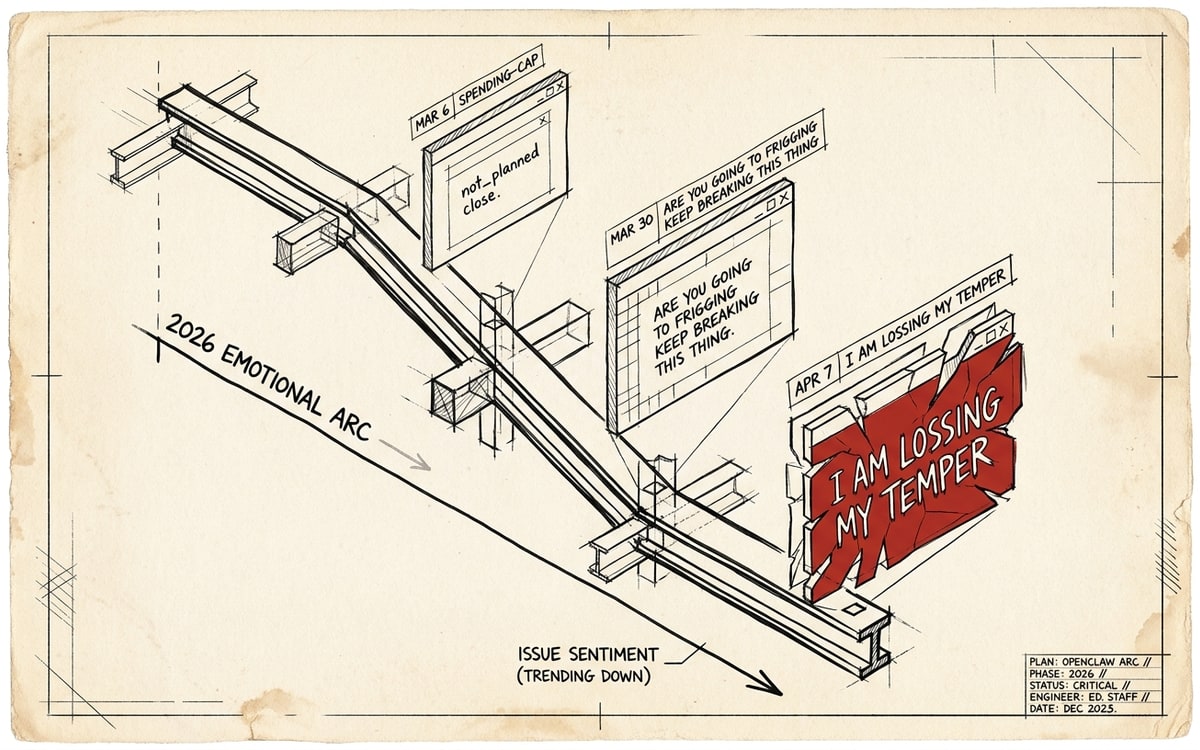
The emotional arc of 2026 is legible in real time on X. OpenClaw started the year in euphoria. Jensen Huang’s GTC quote, “probably the single most important release of software, probably ever,” spread across TechTwitter in March. A YouTube tutorial by Alex Finn titled “The only OpenClaw tutorial you’ll ever need” accumulated 424,200 views and 17,400 likes.
Then the fire season started.
The issue titles that became X screenshots are their own genre. Issue #57898, March 30, from @paciox: “ARE YOU GOING TO FRIGGING KEEP BREAKING THIS THING OR WE CAN GET A STABLE VERSION???????” Issue #62537, April 7: “I AM LOSSING MY TEMPER AND PATIENCE FOR OPENCLAW.” These are not outliers. They represent a community that bought into the euphoria, built workflows on top of the platform, and is now paying for regressions in time and money.
A r/openclaw top post: “Openclaw 202632 is a disgraceful bag of bugs and […]” — stayed at the top of the subreddit for days, quote-tweeted widely.
The HN consensus runs parallel but colder. “It frequently stops responding mid-task. Execution fails without clear recovery. Task success rate feels inconsistent and unpredictable.” The fake-stars debate never fully resolved on HN, but the practical pushback is more damaging: “I don’t use it personally, and neither does anyone in my circle… even though I feel like I’m super plugged into the AI world.” The counter-argument (OpenClaw is #1 on OpenRouter by token volume, 19.9 trillion total) is the only unimpeachable data point OpenClaw has, and it matters: token volume requires real users running real tasks.
Hermes’s reception is different in kind. The community is smaller and in a honeymoon phase. The viral moment was precise: April 12, 7,450 stars in a single day when it hit GitHub’s #1 trending. Chinese tech media covered it with the framing that embedded itself fastest: “Agent中的’爱马仕’” (Tencent News) — Chinese developers call Hermes Agent “爱马仕” (Hermès, the luxury brand), because the pronunciation is similar and the aspiration fits. High-quality, prestigious, not the meme lobster.
@teknium1’s X presence is builder-tone, not influencer-tone. He shares migration tips, compression feature announcements, and retweets community explainers. The contrast with steipete’s charismatic-but-chaotic persona is intentional or at least characteristic: Hermes attracts the ML-serious crowd that OpenClaw’s influencer wave never fully retained. The first wave of credentialed-developer impressions sits in that builder-tone, not in promo-thread shape:
Finally had the chance to get up and running with @NousResearch Hermes Agent and my impression is great.
The thing that has stood out so far: it’s fast, at least twice as fast as OpenClaw (I set up a new instance to test it against)
Generally the UX also just feels a lot better working in the terminal
— @dabit3 April 13, 2026
The GEPA (Genetic-Pareto Prompt Evolution) paper accepted as an ICLR 2026 Oral gave Hermes something OpenClaw never had: peer-reviewed academic credibility for the self-improvement claim. The reaction on the ML research Twitter was immediate. “40% faster at repeated tasks” backed by a citation is different from “40% faster at repeated tasks” in a README.
But the skeptics are accumulating. Early adopters testing Hermes’s self-learning claims in structured experiments are finding that the trajectory is right but the claims are ahead of demonstrated reality. The 9,559 open issues are visible to anyone who looks.
A representative comparison post from a builder running both side by side ends in the same hedged verdict:
Hermes wins 4:1. But I still recommend OpenClaw for most people
Here’s why that’s not a contradiction
I ran both agents across 6 parameters. Here’s what I found:
Setup tie. Both are one-click installs
Memory Hermes. Doesn’t just write files. Uses SQLite+ FTS5 search.
— @Vvtentt101 May 11, 2026
The shape of that verdict is what most builders end up at. Hermes wins on points; OpenClaw wins on accessibility for the next user.
25 SaaS businesses built on their pain
YC called OpenClaw “so hard to set up that even most engineers give up.” This created a market.
There are now at least 25 distinct SaaS businesses offering some version of managed OpenClaw hosting or deployment, with 7+ additional providers for Hermes. None of them existed before January 2026.
The commodity tier (everyone has this): ClawHosted, GetClaw Hosting, RapidClaw, HostedClaws, ClawHosters, Claw-Host.io — all offering “deployed in 5 minutes, no Docker.” Pricing from $24–49/month. Differentiators at this tier are thin: dedicated VPS vs shared infra, UI aesthetics, model selection at signup.
DeployOpenClaw.co claims 400+ customers and a 99.9% uptime SLA — the most credible scale signal in the market. Their credit-pack model for proprietary LLMs is a monetization layer on top of raw hosting that no one else has replicated cleanly.
BetterClaw ($19/month) is the most strategically interesting. It is not a hosting provider — it is positioned as an alternative platform. BetterClaw built a 200-skill audited marketplace after finding 373 actively malicious skills in ClawHub’s 13,700. It ships visual agent building, built-in cost controls, and explicit context-window management. It explicitly targets OpenClaw churn: their blog tracks “openclaw uninstall” as a rising search query and has migration guides for it. Among managed providers, BetterClaw is the company most likely to capture churned users who are not switching to Hermes.
ClawCentral is the most ambitious technical play: 4,000+ MCP tool integrations, per-agent subdomain, TLS certificate, edge-isolated runtime, free tier. Their positioning, “Infrastructure for the AI Agent Era,” is not managed hosting: it is infrastructure for multi-agent systems. This is the right vision but the hardest to execute.
Clawctl ($49/month base) targets the market no one else explicitly addresses: agencies managing 50+ client OpenClaw deployments without hiring DevOps. SOC 2 readiness, SSO, audit logging. White-label: clients see the agency brand, not OpenClaw. $1,500–5,000 agency setup fees with $500–2,000/month per client maintenance at 60–90% margins (OpenClaw is MIT licensed, so there is no license cost). This is real B2B services revenue.
On the Hermes side: FlyHermes ($29.50, stepping to $59/month after first month) is the first-mover and most credible. HermesInstall’s enterprise tier is the most complete — parent billing, private lanes per seat, governed rollout, executive command layer. Featherless.ai bundles Hermes hosting with their own inference, making them the only provider where you get one bill for model + runtime.
The platform integrations: DigitalOcean Marketplace 1-Click, Fly.io official blueprint, Render Blueprint (official docs), Hostinger 1-Click, Railway template, Coolify. The Kubernetes/Helm ecosystem has 191-star and 34-star community charts with documented caveats: OpenClaw is stateful and requires Recreate deployment strategy, NGINX ingress needs 3600-second timeout or WebSockets drop after 60 seconds.
What 25 providers still have not built
The gap analysis across all providers reveals the same five missing pieces, regardless of which tier you look at:
Cost control. Token burn is unpredictable. BetterClaw mentions “cost controls,” ClawCloud tiers by token volume, but no provider ships a per-task budget with automatic kill-switch for runaway loops. The “$47 overnight” stories keep circulating. No managed provider has solved this.
Multi-agent coordination. Every provider hosts one instance. ClawCentral’s MCP marketplace touches it, HostAgentes is building their own multi-agent product (Paperclip) as a hedge. But no provider lets non-engineers configure a team of agents with shared memory and task routing.
Audited skill marketplace. BetterClaw’s 200 audited skills is the only real answer to ClawHub’s malicious skill problem. No Hermes provider has addressed the agentskills.io curation problem at all.
Compliance. SOC 2, HIPAA, GDPR data residency. Only Clawctl and OpenClawPro (DACH) reference these. The enterprise sale cannot close without them.
Agent performance analytics. No provider tells you what the agent accomplished, tasks completed, errors per day, time saved. HermesInstall shows memory and task views but nothing resembling ROI measurement.
The architecture divergence that explains everything
The issue volume, the CVEs, the silent failures, the Curator incident — they all trace back to a single architectural decision made early by each project.
OpenClaw built a gateway: one persistent process that owns everything. Channels, model routing, sessions, plugins, memory, voice — all in the gateway. This is what allows 22 messaging platforms to route through a single runtime. It is also why one memory leak takes down all channels simultaneously, why one CVE exposes the authentication token for every connected session, and why daily releases that touch the gateway touch everything.
Hermes built an autonomous agent with a 15,411-line core file. Everything lives in run_agent.py: prompt assembly, tool dispatch, provider failover, context compression, memory management, streaming, subagent spawning. This is what allows such a wide feature surface in 73 days. It is also why context compression bugs are hard to isolate (they are inside the same file as model routing), why the Curator can corrupt skills without triggering safety checks (it uses the same tool APIs as the main agent), and why silent failures cascade — there is no subsystem boundary to stop them.
Both architectures were correct for the goal they were optimizing for: OpenClaw for multi-channel reach, Hermes for self-improving depth. Both made those goals easier and their opposite goals harder.
The users who suffer most from OpenClaw’s architecture are the ones who need reliability: server deployments that run overnight, workflows where a token loop costs real money, businesses where the gateway going down means zero agent coverage on all channels simultaneously.
The users who suffer most from Hermes’s architecture are the ones who depend on the promise: users who built custom skill libraries that the Curator silently archived, users whose memory fails to persist across sessions despite that being the core product claim, users who trusted the approval gate and found it violated 92% of the time.
Neither architecture is wrong. Both are under-resourced relative to the problem they are trying to solve.
The real opportunity gap
The market has validated demand at every tier: 25+ SaaS providers, 487K combined stars, 19.9 trillion tokens routed. What has not been built is the intersection.
Reliable persistent memory with OpenClaw-grade channel coverage. Hermes has 18 platforms and memory that is non-deterministic in Gateway mode. OpenClaw has 22+ platforms and no default memory at all. The agent that reliably remembers you across sessions and reaches you on every channel has not been built.
A spending-safe agent runtime. Both tools can silently bankrupt users. The feature request for a spending cap was closed as “not_planned” in OpenClaw. Hermes has 73% fixed token overhead with no guardrails. A runtime that treats cost as a first-class metric (hard limits per task, model routing based on cost, anomaly detection for loops) would capture every user who has ever gotten a four-figure API bill from an agent they trusted.
A security-native skill ecosystem. 80% of audited ClawHub skills were malicious. BetterClaw’s 200-skill audited marketplace is the only response, and it is a managed-service moat, not an open ecosystem fix. An agent platform built from day one with code-signed skills, sandboxed execution, and supply-chain auditing would be the first in the category to take this seriously.
The managed platform that survives its runtimes. The 25 SaaS providers are all betting that OpenClaw or Hermes stays relevant. BetterClaw is hedging by building a platform that abstracts over the runtime — they run OpenClaw today and could run Hermes or something else tomorrow. HostAgentes is building Paperclip as their own multi-agent product. These are the companies that understand the real business: not managed hosting, but the interface layer between non-technical users and whatever agent runtime is winning this month.
The runtime wars will keep going. ClawCharts tracks 11 repos now. Hermes’s weekly growth (+13.2% this week, after +63% the prior week) is flattening from the spike: the organic portion of the growth is still real but the viral acceleration is over. OpenClaw’s growth is baseline. Neither is going away. Both are accruing the kind of institutional debt (open issues, unfixed CVEs, architectural decisions made at speed) that creates the opening for something more considered.
487,664 stars. 57,000 issues. The stars said one thing. The issues said everything else.